XyDromatics Identity Trust
Generally available
Identity directory · Standards-compliant LDAPv3

XyDromatics Identity Trust — one directory for the whole shop.

Create every user account once, and every application in the building authenticates against it — instead of each application keeping its own separate list of logins.

Built for smaller facilities that never stood up a corporate directory: a single self-contained server, an admin console to manage people and groups, and standard LDAP so any application — the Synthology fleet included — can point at it.

Request a demo
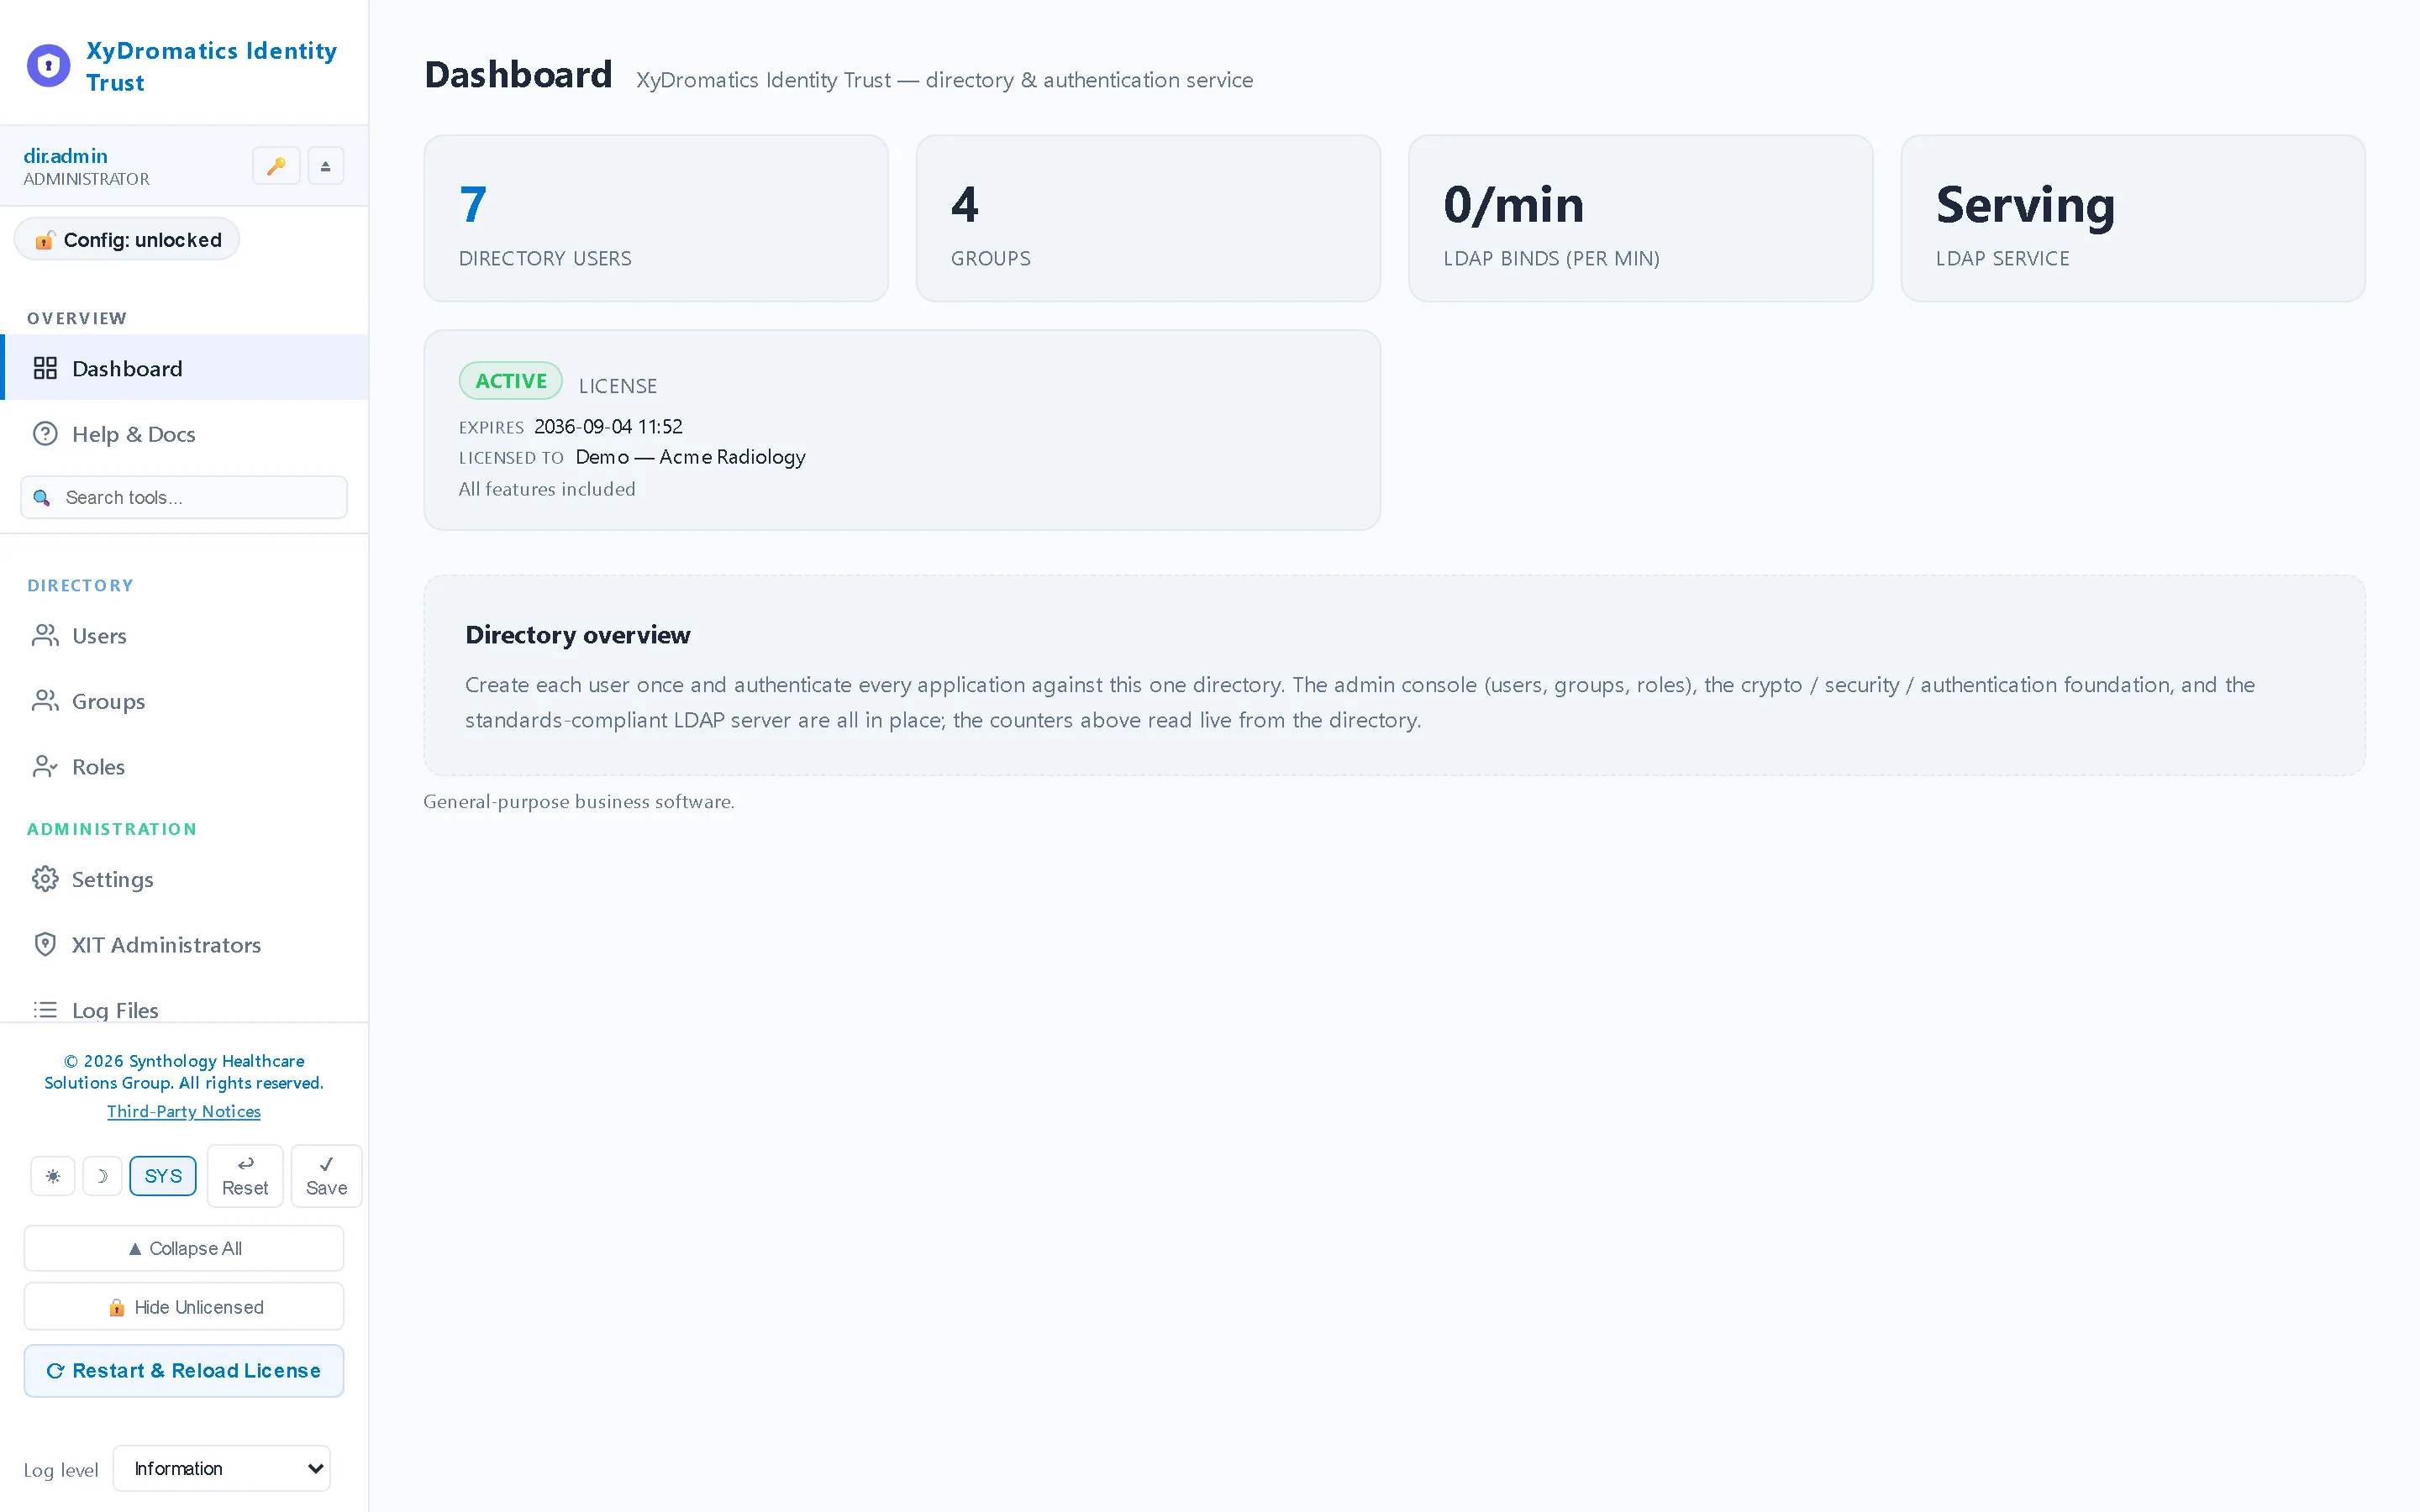
Dashboard — Directory health, LDAP serve state, bind activity and the fleet applications trusting this directory — on one screen.
Dashboard. Directory health, LDAP serve state, bind activity and the fleet applications trusting this directory — on one screen.
))}

At a glance

Availability
Generally available
Classification
General-purpose business software
Protocol
LDAPv3 over TLS
Storage
SQLite (default) · PostgreSQL
Platforms
Windows · Linux
Best for
Facilities with no existing directory
Full regulatory posture →

The problem it solves

The same people, re-created in every application.

Without a directory

A smaller facility that never stood up a corporate directory ends up with a separate list of user accounts inside every application. The same person is entered over and over, each with its own password to remember and reset.

When someone leaves, an administrator has to remember every application they were in and disable each one by hand. Miss one and access lingers.

With Identity Trust

Every user lives in one directory. Each application binds to it over standard LDAP, so people sign in with a single account managed in a single place.

Onboard once, and it works everywhere. Disable once, and access is gone everywhere — no per-application cleanup to forget.

What it does

A directory that fits a smaller shop.

Standard on the wire, simple to run, and something every application you already own can talk to.

One directory, standard protocol

Speaks the protocol every application already knows.

  • Standards-compliant LDAPv3 — any LDAP-aware application can bind to it, not just Synthology software
  • inetOrgPerson people and groupOfNames groups, with memberOf for group membership
  • Simple bind, RFC-4515 search filters, Password-Modify, and paged results
  • LDAPS and StartTLS — encrypted on the wire
Run it anywhere, manage it simply

A single self-contained server, sized to the building.

  • One self-contained server — no separate database engine to stand up
  • SQLite by default; choose PostgreSQL for a replicated, highly-available pair
  • An admin console is the primary way to add people, reset passwords, and manage groups
  • Manager-DN binds for scripted provisioning when you would rather automate
  • Windows and Linux — the same product installs the same on both

Create a user once

The whole point: stop re-creating the same people everywhere.

  • Add each employee a single time, in one place
  • Every application authenticates against the same directory
  • Disable someone once and they lose access across every connected application
  • Groups drive who can do what, consistently across the shop

The Synthology fleet, by configuration

Every Synthology product already knows how to bind to it.

  • Each Synthology product points its built-in LDAP client at the directory
  • Adoption is configuration, not custom work — nothing to build per application
  • Group membership maps to each product’s roles
  • Your other LDAP-aware line-of-business software can bind to the very same directory

See it

One directory, every application — on screen.

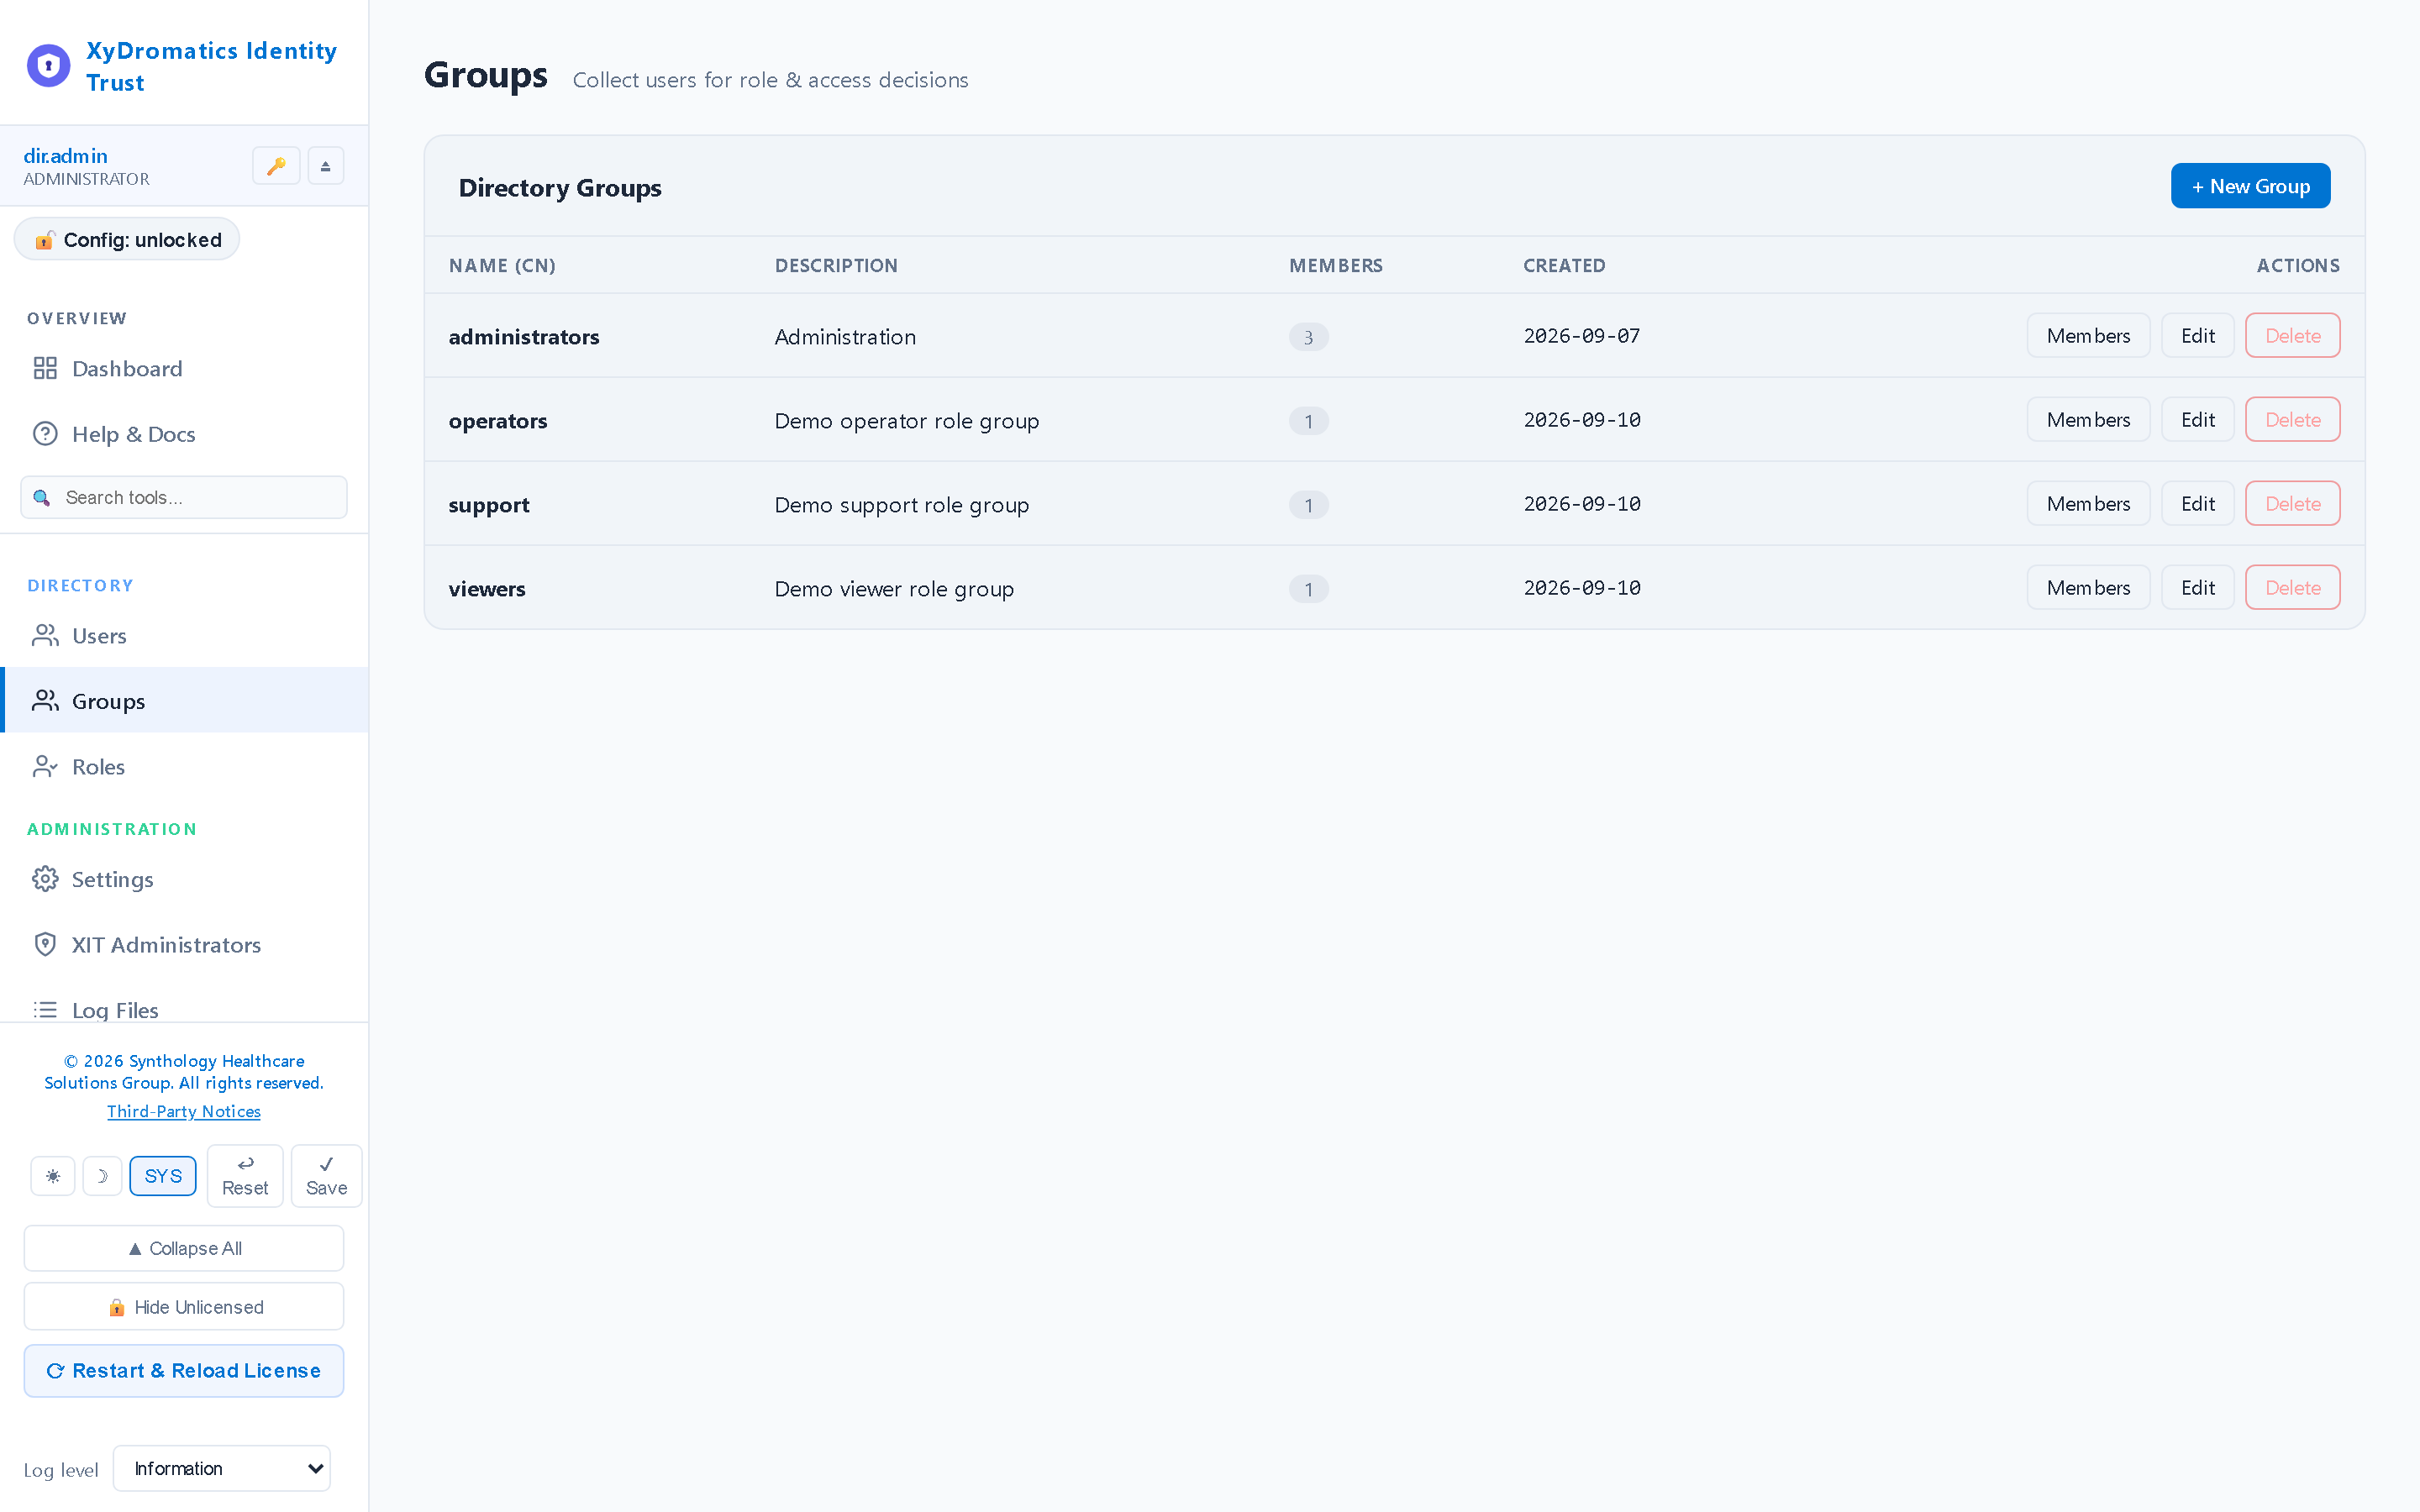
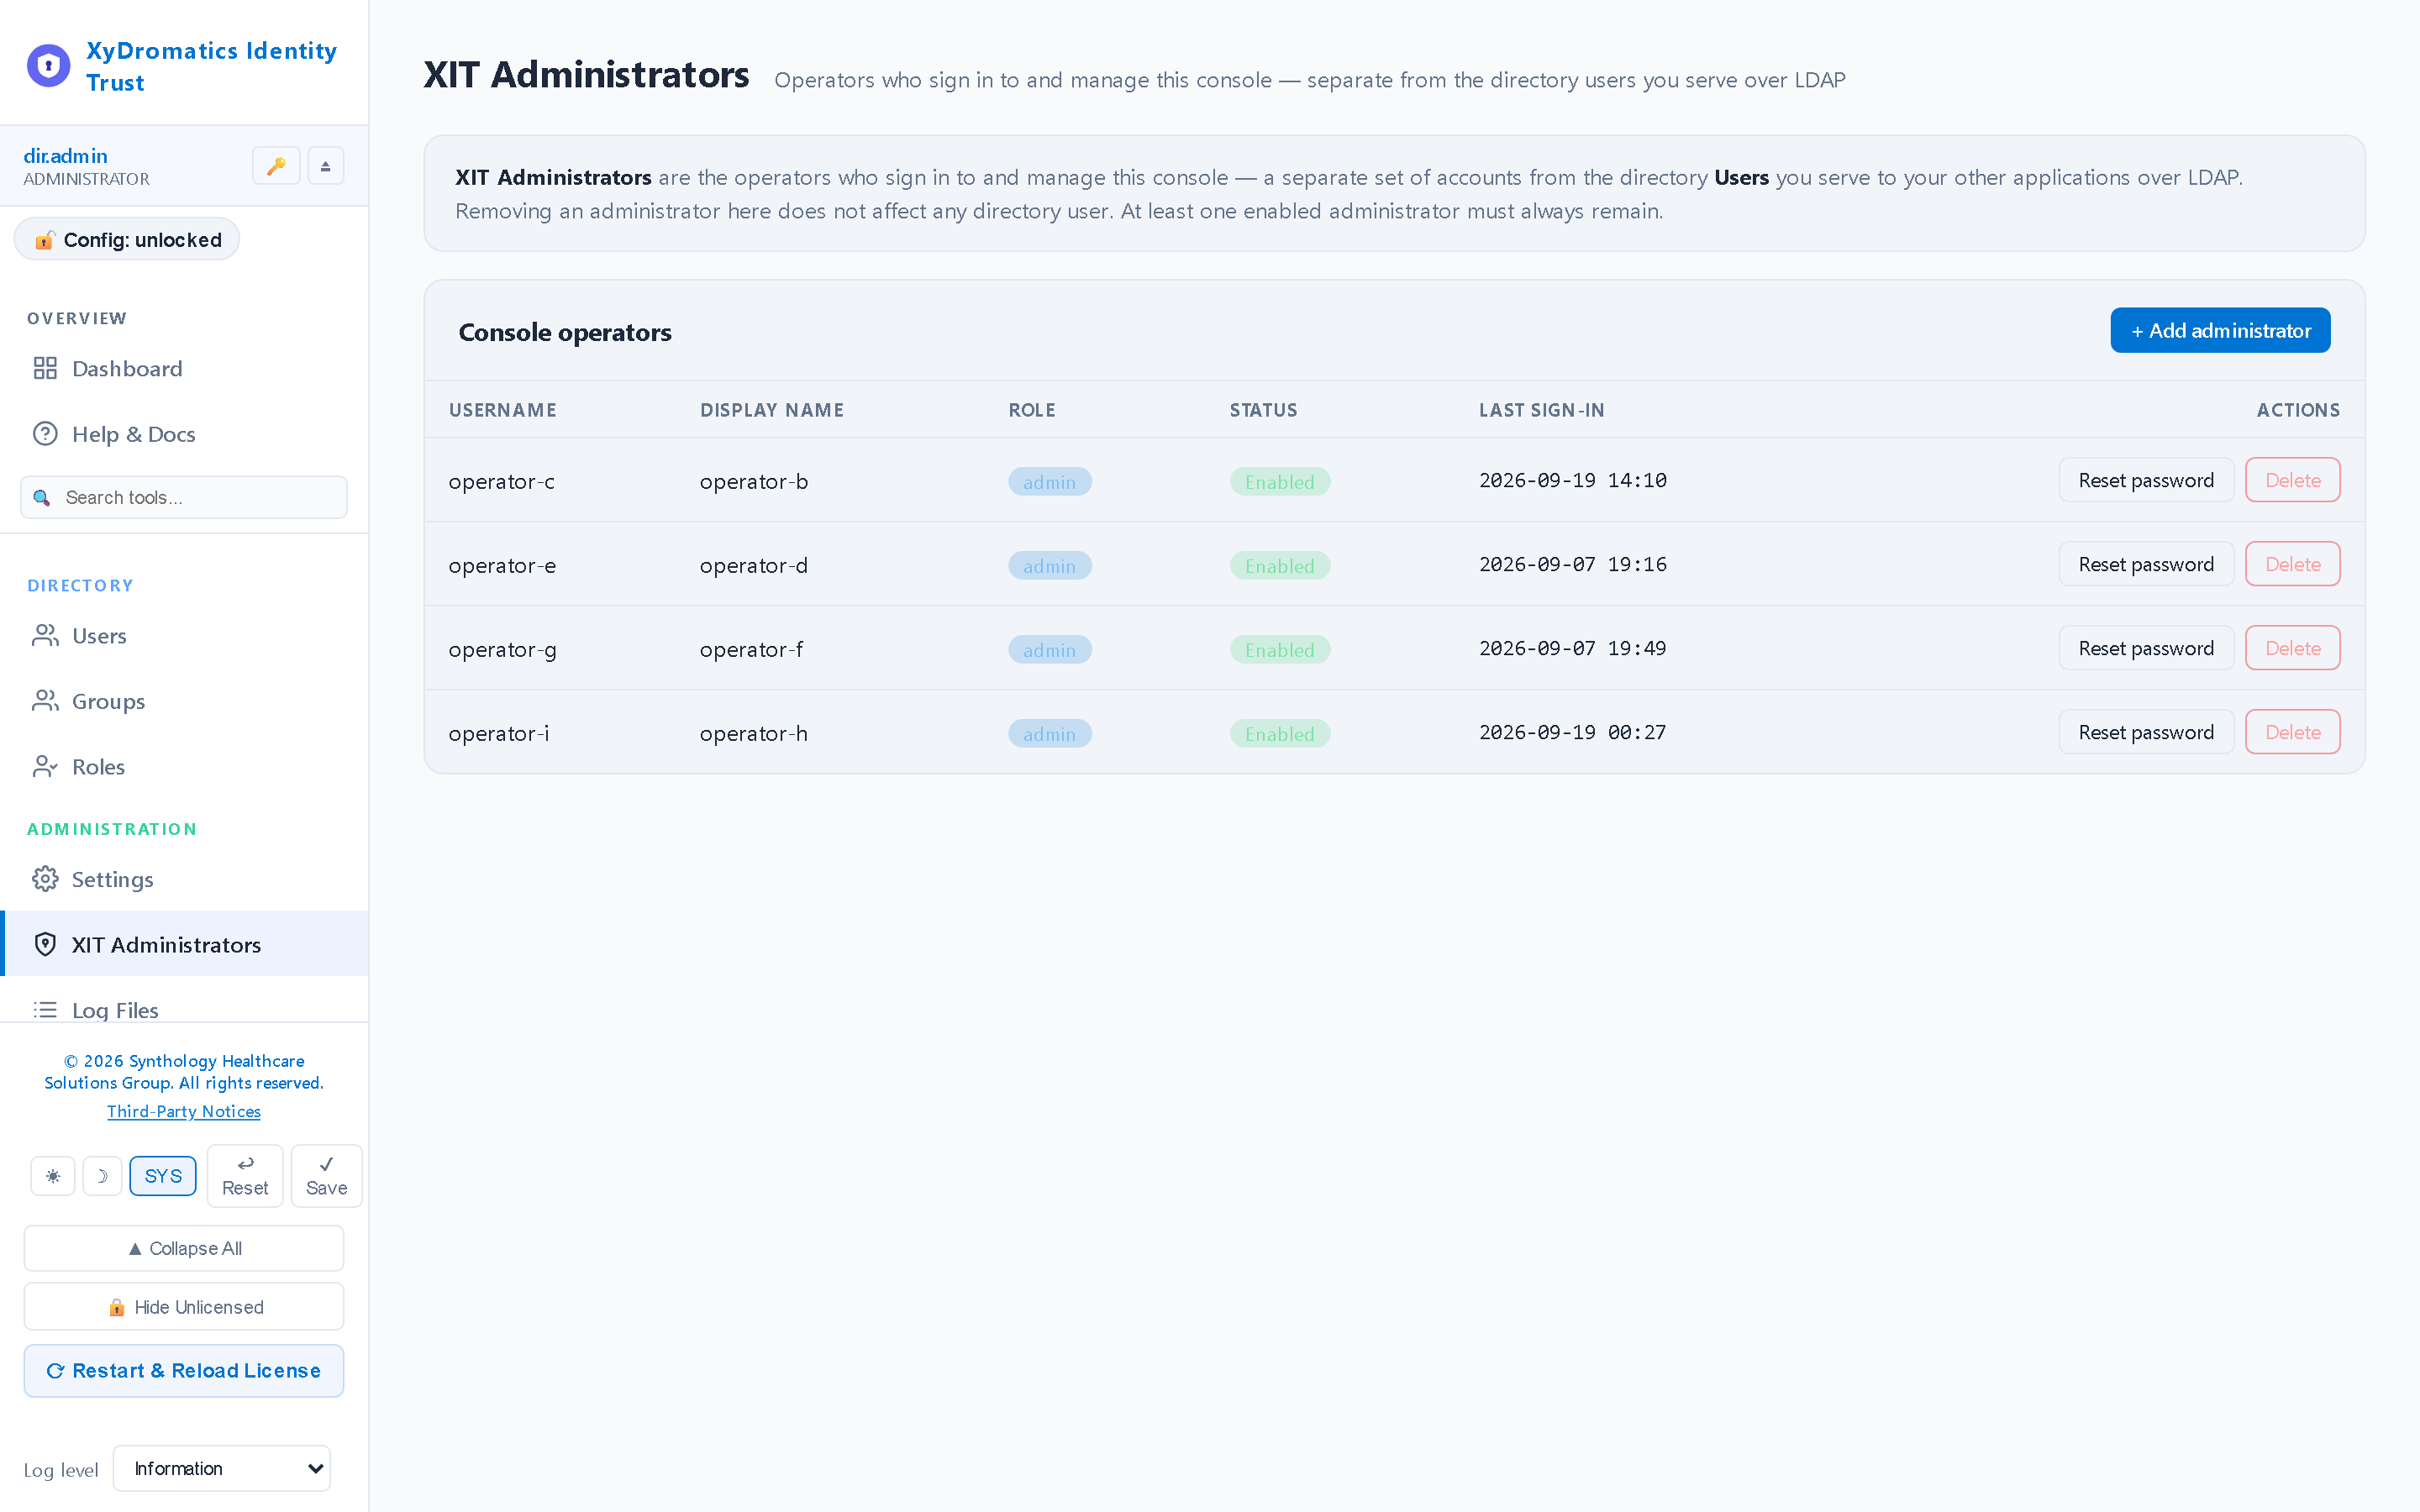
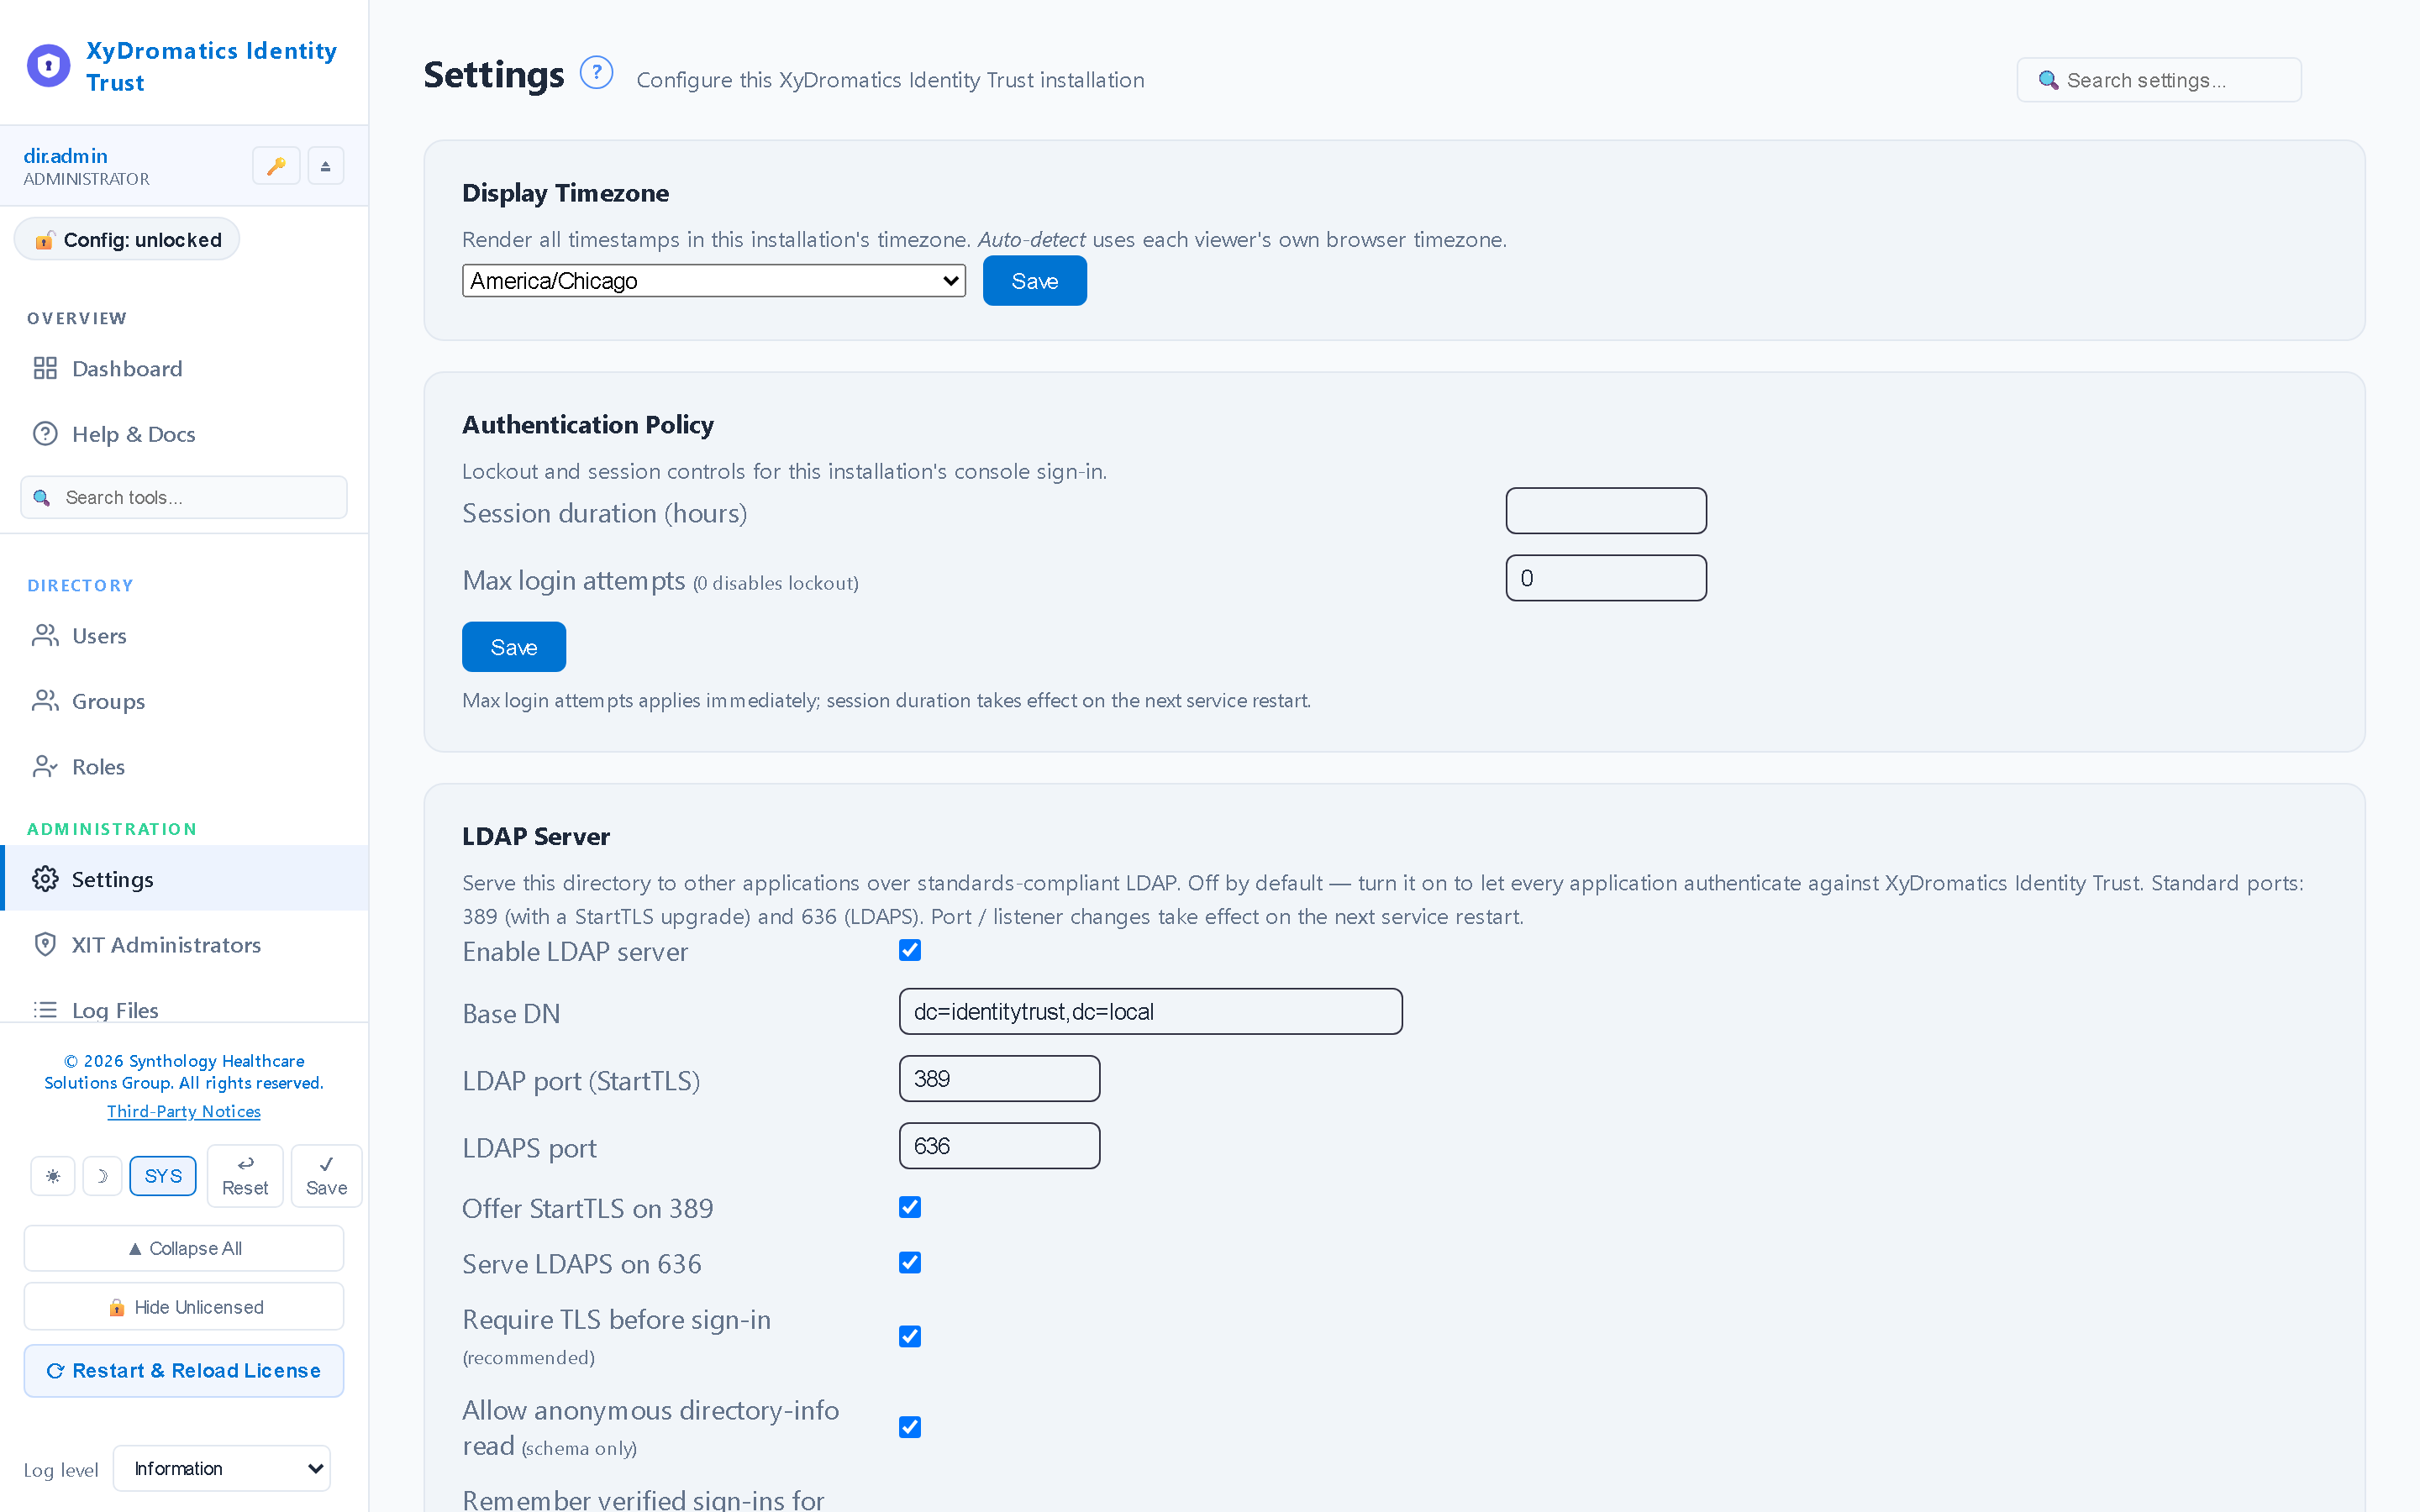
Live captures from a running installation — click any screen to enlarge it.

01

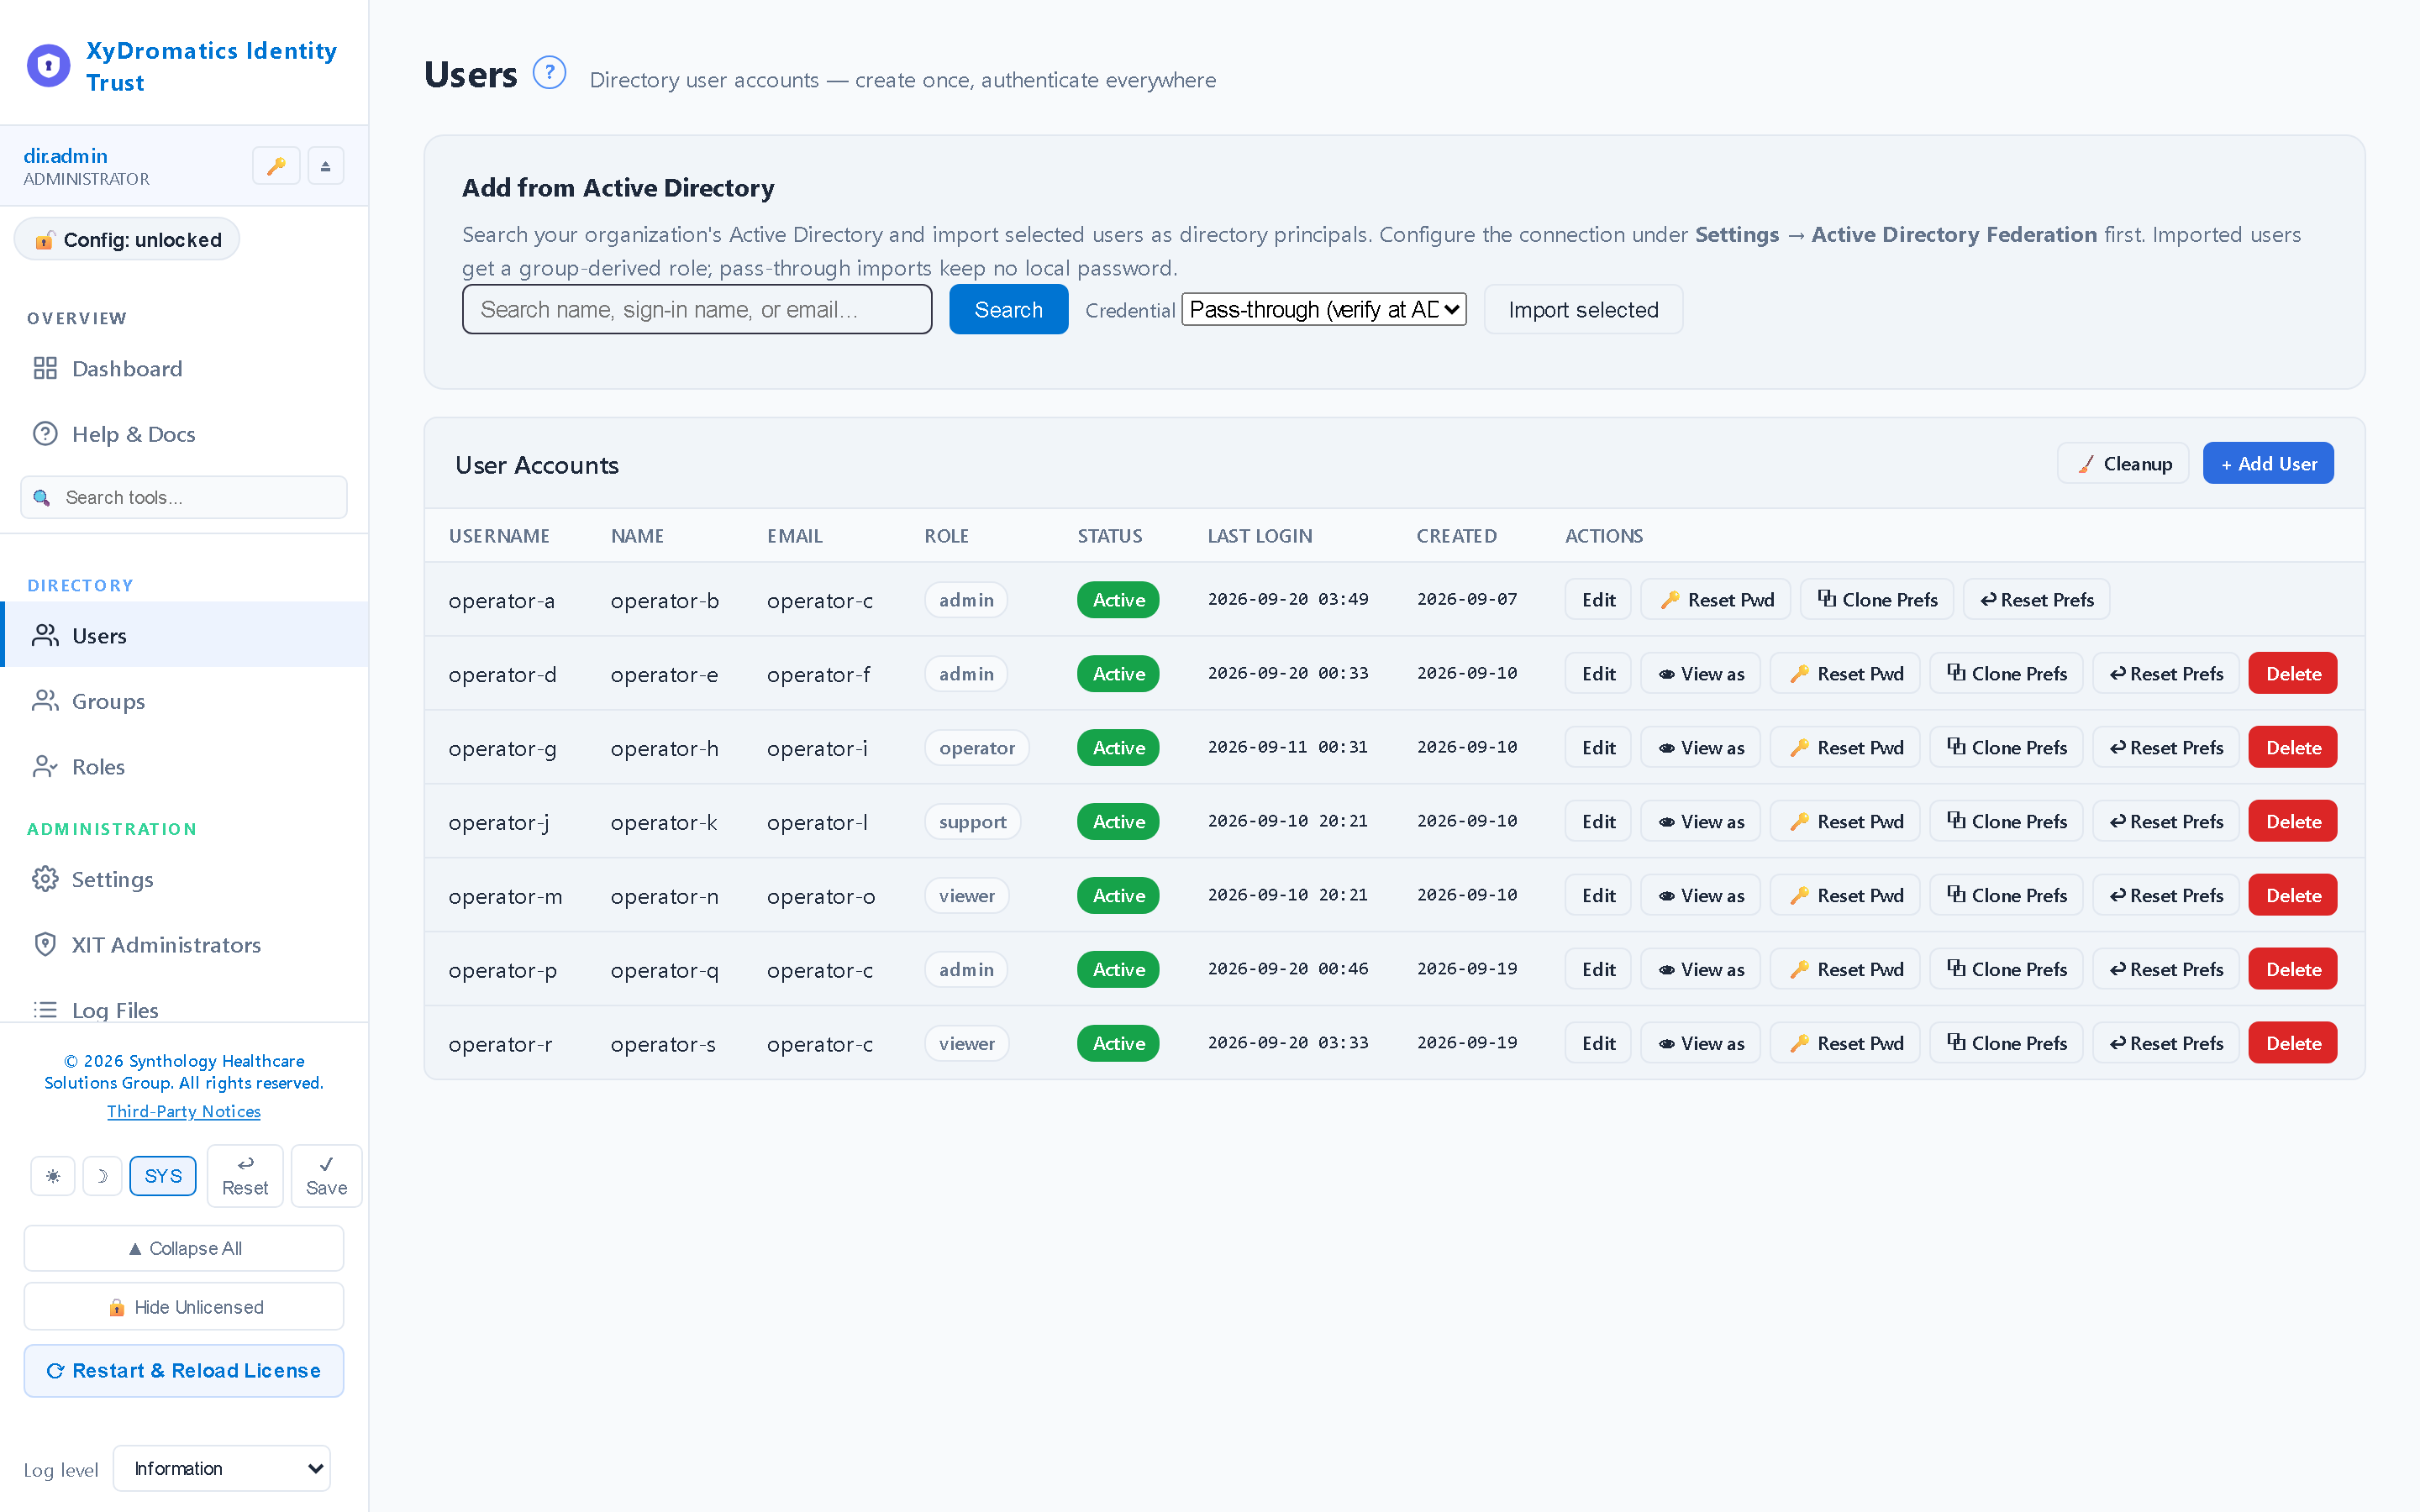
Users

The people every XyDromatics application authenticates — one identity, served over LDAP.

02

Groups

Groups map to application roles, so an operator gets the same access on every product.

03

Console administrators

Who can administer the directory itself — separate from directory membership.

04

Settings

LDAP / LDAPS listener, TLS, base DN and the service accounts each application binds with.

Availability

Generally available.

Identity Trust is generally available now, covering the capabilities on this page: a standards-compliant LDAPv3 server, the admin console, SQLite and PostgreSQL storage, and Windows and Linux installers.

If a single directory for your facility is on your list, request a demo and we will walk you through it.

Documentation

The controlled-document set.

Current GA release v1.0.1.30 · released 2026-09-19

Every XyDromatics Identity Trust deployment ships with the documents below, all managed under SynthQMS document control. Identity Trust is a directory (LDAP) service, not a DICOM product, so it carries no DICOM Conformance Statement; the documents are shared under mutual NDA.

What’s new·v1.0.1.30

One directory for every application — first general availability

  • Create each user once, then sign in to every application on your network against a single standards-compliant LDAP directory — no more per-application account sprawl.
  • Run standalone for a small facility, or federate to an existing Active Directory / LDAP so the directory you already have stays the source of truth.
  • Portable, encrypted configuration bundles make backup, migration, and disaster recovery a single-file operation.
  • Comprehensive in-app help — each topic explains what the page does, how to do it, a worked example, and the permission it requires — including a guided installation walkthrough.
  • Ships with the approved End-User License Agreement and clears a full QA + security-test pass on the release build. General-purpose business software; not a medical device.
Document Title Notes
DOC-2026-511 Hardware & Software Requirements (Identity Trust) Sizing, OS support, dependencies
DOC-2026-514 EULA Annex (Identity Trust) Annex to the Synthology Master EULA (DOC-2026-063)
DOC-2026-513 Internal Security Assessment / Penetration Test (Identity Trust) Available under NDA
DOC-2026-512 QA Runner Manual (Identity Trust) Internal QA + customer-validated test runs
DOC-2026-509 End User Guide (Identity Trust) Operator + administrator workflows
DOC-2026-510 Installation Guide (Identity Trust) Includes MSI deploy + Linux tarball install

Additional documents

XyDromatics Identity Trust-specific documents beyond the standard set. Items marked Pending are tracked for authoring under SynthQMS change control.

Document Title Notes
DOC-2026-515 Third-Party Software Attribution (Identity Trust) Open-source components + licences

One place for every login.

XyDromatics Identity Trust gives a facility a single directory that every application — the Synthology fleet included — authenticates against. Generally available now for Windows and Linux.